
Blog
Practical advice on websites, security, SEO, CRM and AI for service businesses — from our YouTube channel.
-
Jira & Confluence Attacks Have Started – What Changed Overnight?
Exploitation attempts have begun against self-hosted Jira and Confluence, plus the PoeLLM AI server campaign, Cisco License On-Prem, WordPress Events Manager and an Express…
Read more -
WordPress 7.1.3 Security Update – What Website Owners Need to Do Today
WordPress 7.1.3 fixes seven core security issues, plus active attacks on Ninja Forms and Rejetto, an Atlassian file exposure risk and a Payload CMS…
Read more -
Trusted npm Package Compromised – Developer & Cloud Credentials at Risk
A compromised SubQuery npm package, a new exploited Citrix NetScaler flaw, chained Zammad vulnerabilities, a Cloudflare API Shield incident and WordPress image upload risks…
Read more -
An AI Agent Accessed Another Australian Government Website
An OpenAI agent accessed a NSW National Parks fire-history application, plus vulnerabilities in ZITADEL, Mammoth.js, Ultimate Member and WP Statistics, and what to check…
Read more -
Critical n8n + Supabase Flaw: Check Your Workflows Today
A critical n8n and Supabase flaw, self-rebuilding WordPress malware, a vm2 sandbox bypass, Apache 2.4.69 fixes and a BackupSheep plugin vulnerability: five security stories…
Read more -
Citrix NetScaler Is Being Exploited – Plus 7 Next.js Fixes
Citrix NetScaler is being exploited in Australia, plus seven Next.js fixes, a critical TanStack Start flaw, long-hidden malicious npm packages and a Zella WooCommerce…
Read more -
Stolen AI API Keys + 101 Malicious npm Packages
ASD warns stolen AI API keys are being abused, plus a nine-vulnerability Next.js release, 101 malicious npm packages, a Drupal API authentication flaw and…
Read more -
WordPress Plugin on 1M+ Sites Left Database Backups Public
File Manager left WordPress database backups publicly downloadable, plus flaws in WPForms, Bookly, Paymattic, Verge3D, Blacklist Manager and WP Review Slider Pro, and what…
Read more -
WooCommerce Quote Plugin Flaw: Hackers Upload PHP, No Login
A critical Request a Quote for WooCommerce flaw lets attackers upload PHP without logging in, plus vulnerabilities in Better Messages, Automatic.css and Bookly, and…
Read more -
Manage WordPress Like an Agency: Why Updates Aren’t Enough
Clicking update doesn't prove your WordPress site is secure, working or uncompromised. This new series shows how an agency manages WordPress beyond simple updates.
Read more -
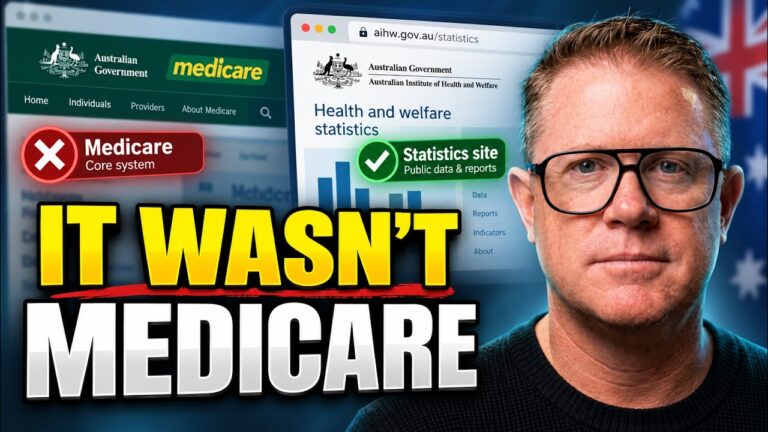
Did OpenAI Hack Medicare? What Actually Happened
An OpenAI agent didn't hack Australians' medical records, but it did bypass controls on a decades-old Medicare statistics portal. Here's what actually happened and…
Read more -
WordPress 7.1.2 Attacks Have Started – Check Your Site Now
Attacks on the WordPress 7.1.2 core flaw have moved to writing PHP files onto servers. Plus WP OAuth Server, cPanel WP Toolkit, must-use plugin…
Read more